Data confidentiality & model governance
Replicant includes native protections that help enterprises meet data residency, privacy, and compliance obligations—without needing external tools.
Automatic redaction
Protect sensitive data across transcripts, logs, and QA analytics.
Granular access control
Manage permissions with full audit trails and transparency.
Secure LLM governance
Customer data is never retained, reused, or used for training.
Industry-leading frameworks like the OWASP Top 10 are embedded into every stage of our development lifecycle.
Safe use of Generative AI
Replicant enforces comprehensive controls to support enterprise deployment of LLMs for mission-critical applications.
Exhaustive security testing
Test for jailbreaks, hallucinations, and misuse.
Brand-safe outputs
Maintain consistency through prompt testing and model guardrails.
Pre-approved responses
Prevent hallucinations in high-risk workflows.
Full audit visibility
See what the AI said, why it responded, and what triggered it.
Our enterprise-grade platform adheres to the NIST Cybersecurity Framework (CSF) and the NIST AI Risk Management Framework (AI RMF).
Data protection
GDPR compliance
Replicant’s platform is fully aligned with the requirements of the General Data Protection Regulation (GDPR), supporting global customer service operations.
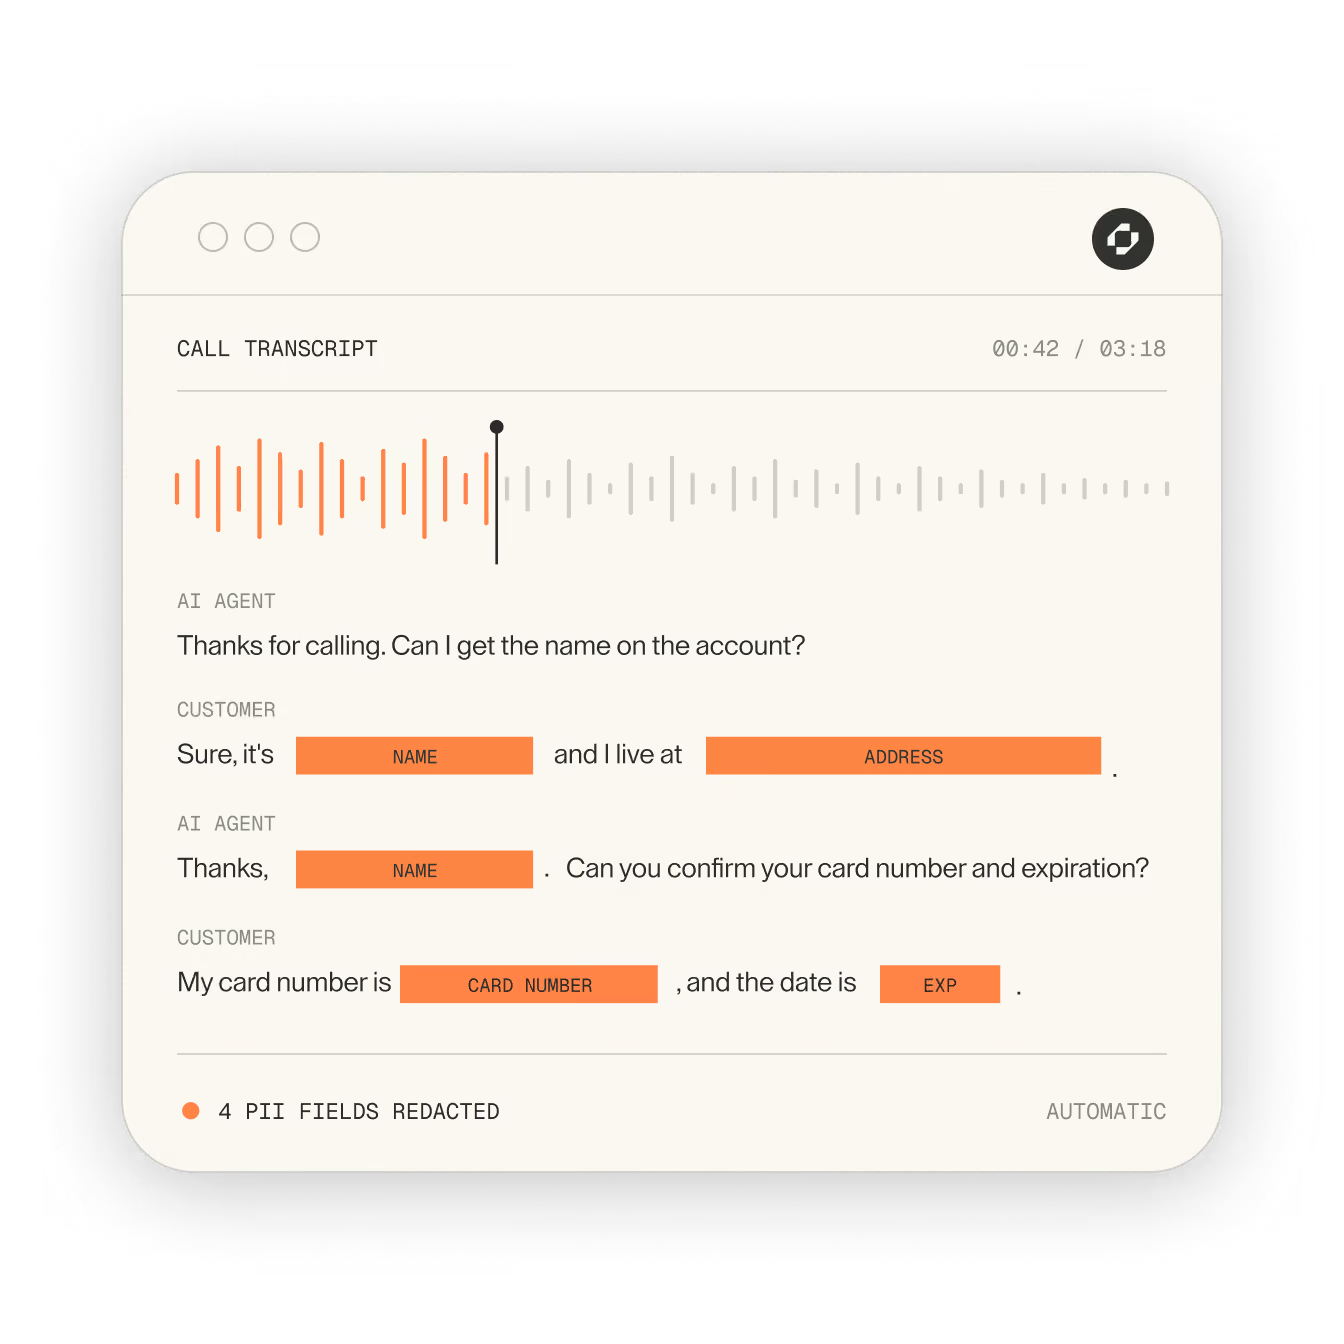
Sensitive data, scrubbed automatically.
Personally Identifiable Information (PII), payment information, and other sensitive customer inputs are automatically redacted from AI interactions, call transcripts, analytics logs, and QA workflows.
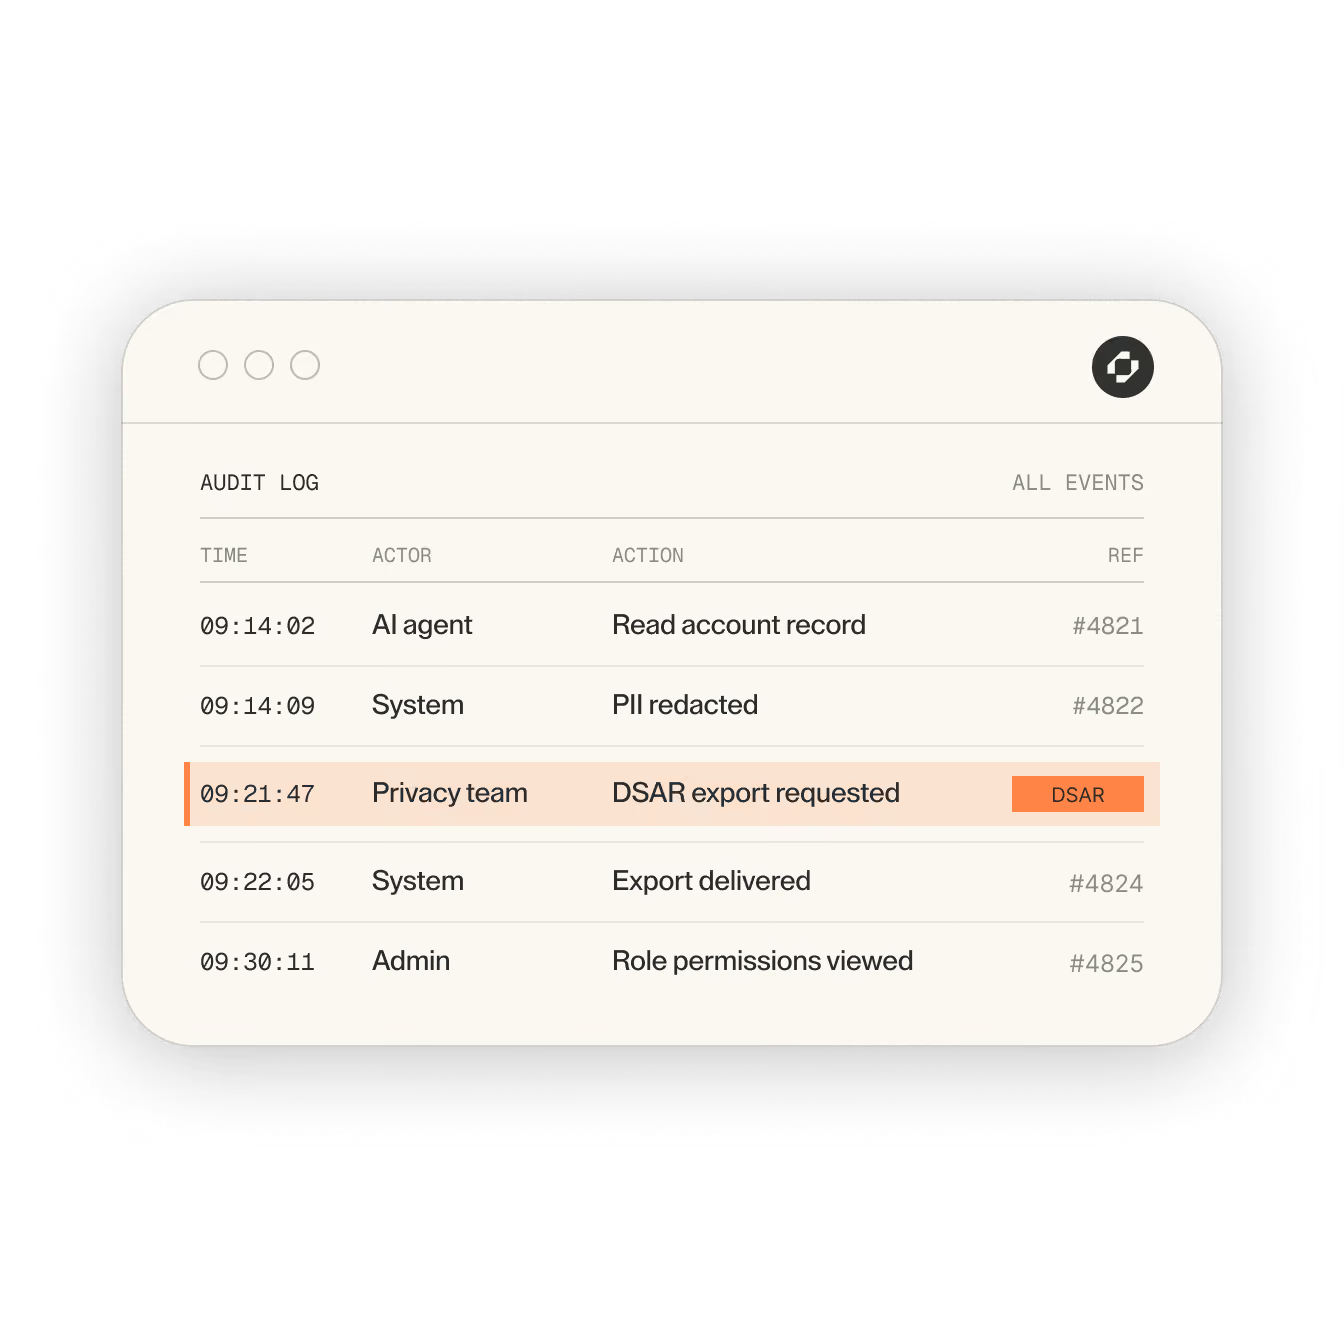
Every touchpoint, logged and traceable.
Every interaction with customer data is logged and traceable, ensuring accountability and enabling rapid response to Data Subject Access Requests (DSARs).
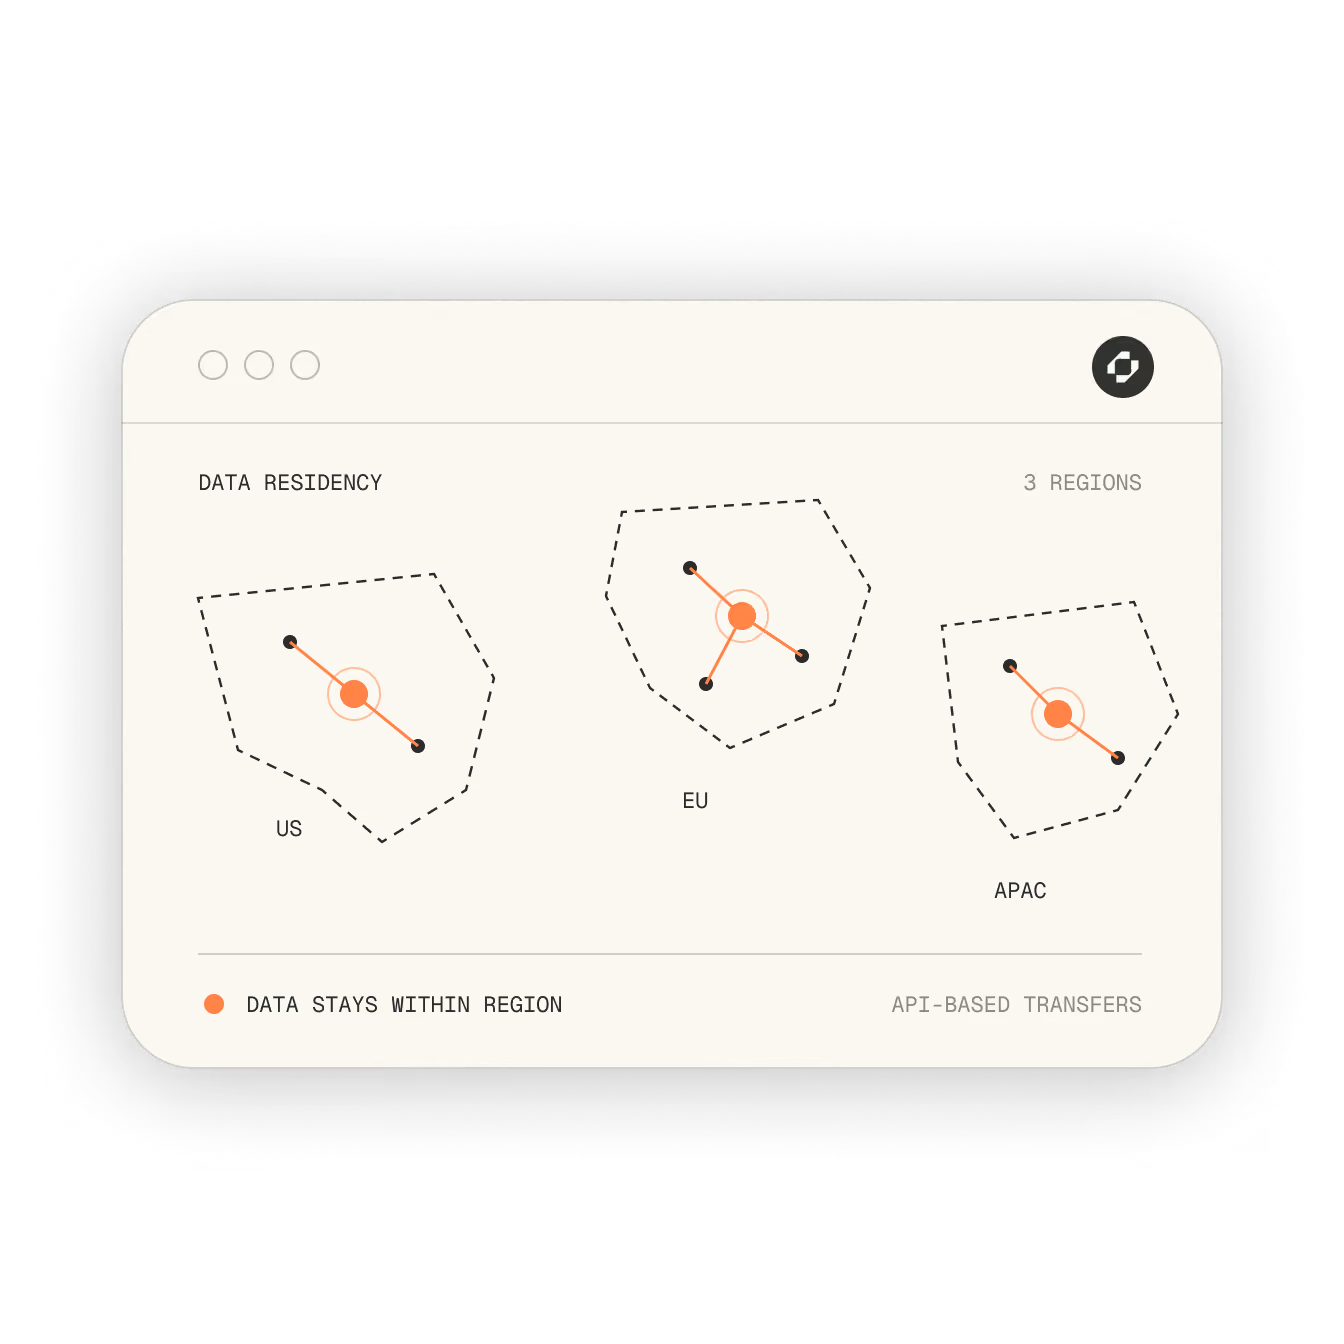
Your data, wherever it needs to stay.
Replicant supports secure API-based transfers that maintain data residency boundaries and comply with cross-border requirements under GDPR and similar frameworks.
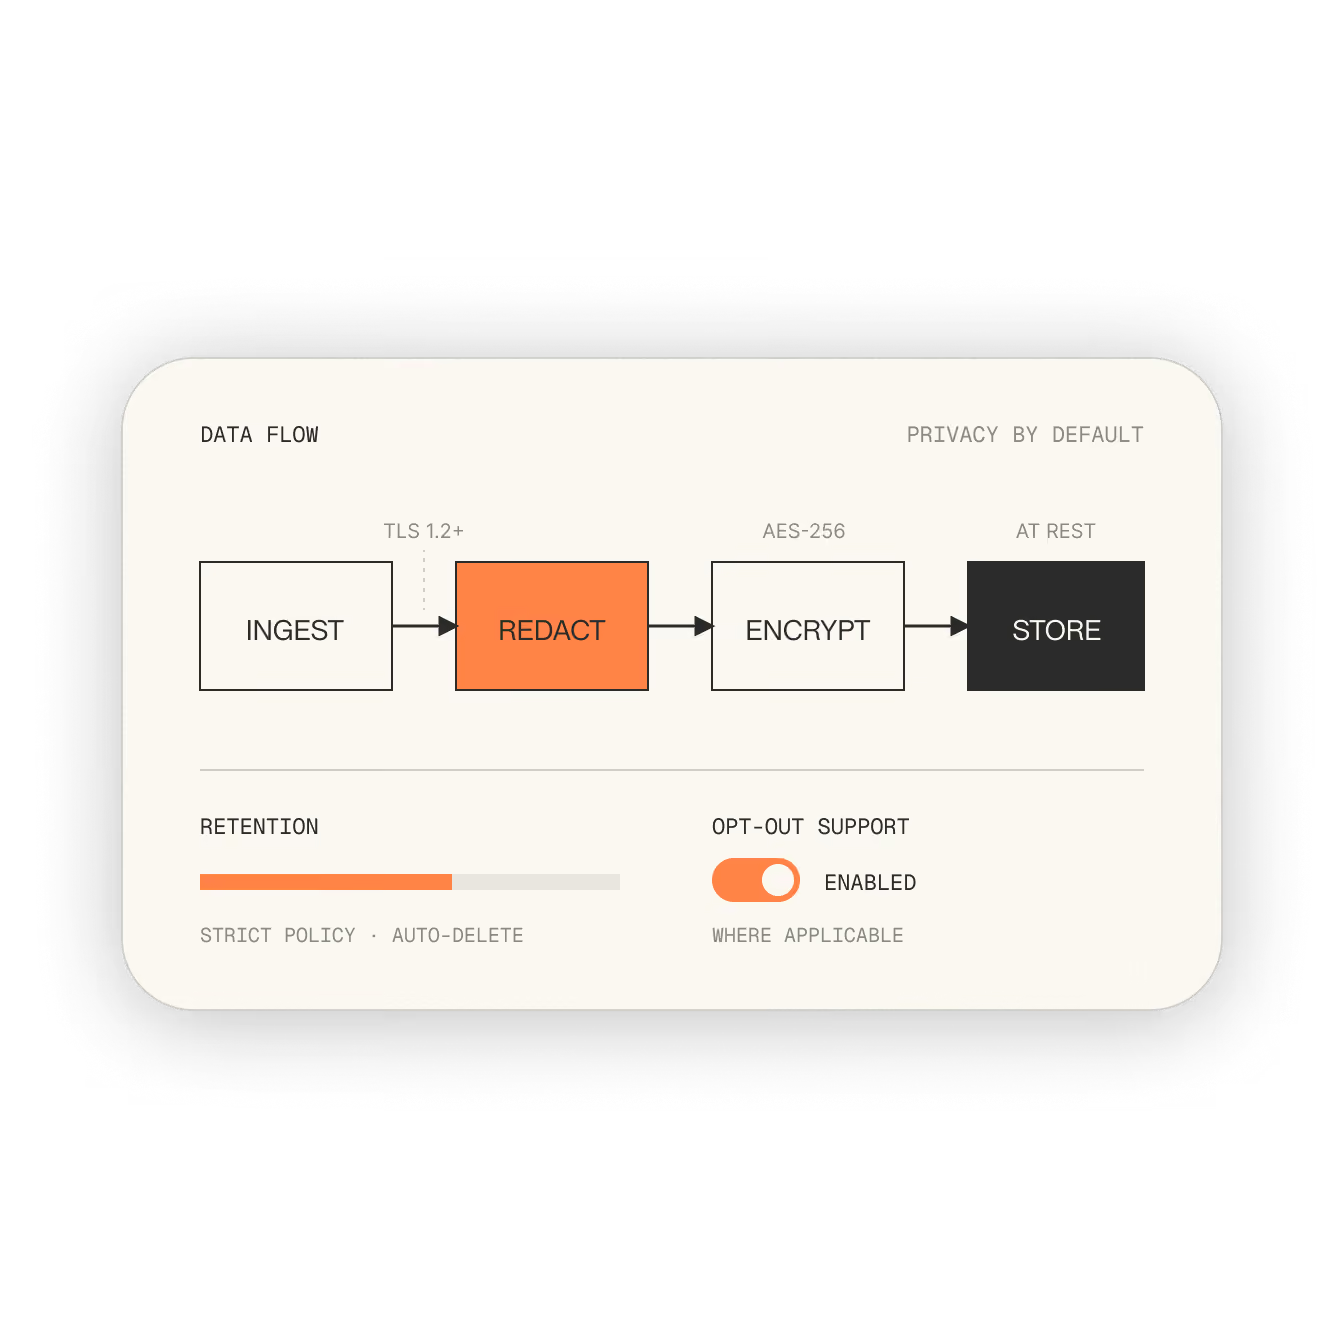
Privacy isn't a setting. It's the architecture.
Replicant’s platform is engineered with GDPR’s “privacy by design and by default” principles. This includes encrypted storage and transport (AES-256 and TLS 1.2+), strict retention controls, and opt-out support where applicable.
Testimonials
How it works
Infrastructure-level security
Replicant captures and analyzes 100% of conversations across channels and agents for full traceability and auditability.
SOC 2 Type 2, PCI DSS, HIPAA certifications — independently validated.
TLS 1.2+ and AES-256 encryption for all data in transit and at rest.
Intrusion Detection & Prevention Systems (IDPS) and continuous threat monitoring.
Role-Based Access Control (RBAC) with Multi-Factor Authentication (MFA) built in.
COmpare
Security by default.
Built for enterprises that can't afford to gamble on data protection.
Partial or layered encryption leaves exposure between systems.
PII scrubbing is missing or left to human review.
Basic permissions with little granularity.
Multi-vendor failover rarely implemented end-to-end.
Shared models with unclear training or controls.
Informal or incomplete certification coverage.
Encryption built in from the ground up, not bolted on.
Automatic, default across every data type.
Enforced access controls down to the individual level.
Failover across telephony, TTS, and LLM.
No public training, full audit visibility.
SOC 2, HIPAA, PCI DSS, GDPR.